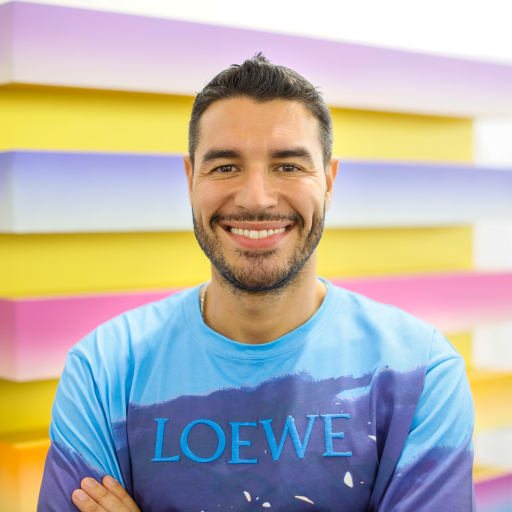
Hello! My name is Matt Suiche. I work on AI Security at Tolmo, and I also experiment with side projects in AI Safety (Weightless, etc.) and Emulation & Operating System Research (WASM PSX, WASM NanoKrnl, etc.). I recently discussed cyberwar in the age of AI, Iran’s cyber capabilities, and how AI is reshaping hacking on Bloomberg’s Odd Lots and the National Security Lab podcast.
Previously, I founded OnDB Inc., a data infrastructure startup for the agentic economy, and co-founded CloudVolumes (acquired by VMware in 2014) and Comae Technologies (acquired by Magnet Forensics in 2022), where I later served as Head of Detection Engineering. I also founded the cybersecurity community project OPCDE.
My path into technology started in reverse engineering as a teenager, and has since spanned memory forensics, operating systems, virtualization, blockchain, and now AI infrastructure.
The prompt you type into at nanokrnl.ai runs the real Microsoft cmd.exe, sort.exe, where.exe, whoami.exe and more.com, unmodified, on a from-scratch Rust NT kernel's own syscalls. Here is what it takes to load a real .exe, give it handles, …
nanokrnl has no disk. It runs in a browser tab. So how does 'more H:\readme.txt' read a real file? The answer is 9P, the Plan 9 protocol that Linux and WSL2 use to share a host filesystem into a guest. This post walks the transport, the …
nanokrnl is an NT-shaped kernel in Rust that boots in a browser tab through nanox, a 65 KB x86-64 emulator we wrote from scratch. This first post in a nanokrnl and nanox series walks the two ways it boots, how the whole machine is …