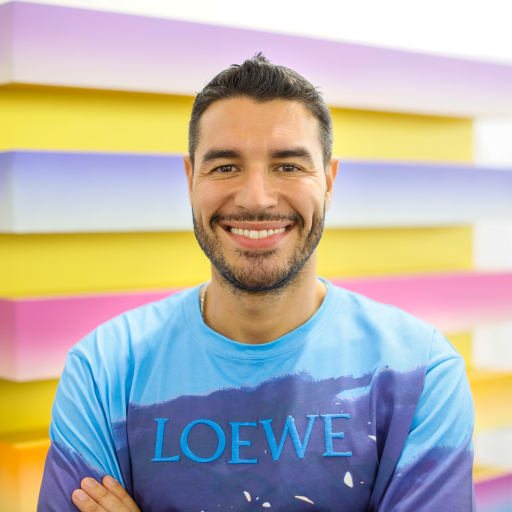
Hello! My name is Matt Suiche. I work on AI Security at Tolmo, and I also experiment with side projects in AI Safety (Weightless, etc.) and Emulation & Operating System Research (WASM PSX, WASM NanoKrnl, etc.). I recently discussed cyberwar in the age of AI, Iran’s cyber capabilities, and how AI is reshaping hacking on Bloomberg’s Odd Lots and the National Security Lab podcast.
Previously, I founded OnDB Inc., a data infrastructure startup for the agentic economy, and co-founded CloudVolumes (acquired by VMware in 2014) and Comae Technologies (acquired by Magnet Forensics in 2022), where I later served as Head of Detection Engineering. I also founded the cybersecurity community project OPCDE.
My path into technology started in reverse engineering as a teenager, and has since spanned memory forensics, operating systems, virtualization, blockchain, and now AI infrastructure.
Potential links to North Korea have been found.# Read More: Part 1 — Part 2 — Part 3 — Part 4
Code similarities are shared between a February 2017 sample of WannaCry and 2015 Contopee sample (previously attributed last year to Lazarus …
One new wave stopped today but the worse is yet to come# Read More: Part 1 — Part 2 — Part 3 — Part 4 @msuiche (Twitter)
UPDATE: Latest development (15May): Attribution and links to Lazarus Group
UPDATE2: — Decrypting files
As a follow-up …
More than 70 countries are reported to be infected.# Read More: Part 1 — Part 2 — Part 3 — Part 4 — @msuiche (Twitter)
UPDATE: Latest development (15May): Links to Lazarus Group
UPDATE2: — Decrypting files
IMPORTANT NOTE: Microsoft released …