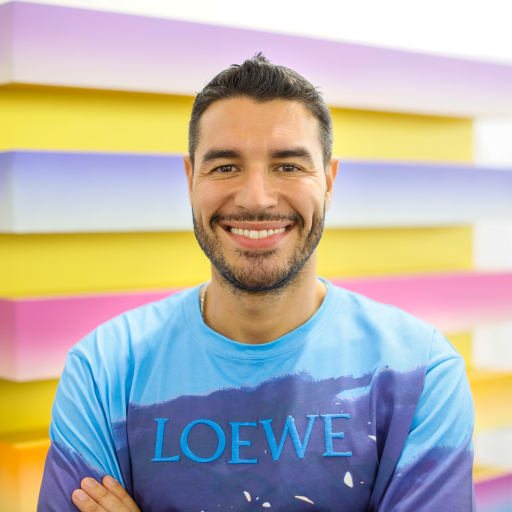
Hello! My name is Matt Suiche. I work on AI Security at Tolmo, and I also experiment with side projects in AI Safety (Weightless, etc.) and Emulation & Operating System Research (WASM PSX, WASM NanoKrnl, etc.). I recently discussed cyberwar in the age of AI, Iran’s cyber capabilities, and how AI is reshaping hacking on Bloomberg’s Odd Lots and the National Security Lab podcast.
Previously, I founded OnDB Inc., a data infrastructure startup for the agentic economy, and co-founded CloudVolumes (acquired by VMware in 2014) and Comae Technologies (acquired by Magnet Forensics in 2022), where I later served as Head of Detection Engineering. I also founded the cybersecurity community project OPCDE.
My path into technology started in reverse engineering as a teenager, and has since spanned memory forensics, operating systems, virtualization, blockchain, and now AI infrastructure.
What we know so far about Byata.# Summary# Yes, this is bad — real bad — this is another ransom-ware leveraging SMB network kernel vulnerabilities to spread on the local network. The exploit used is based on ETERNALBLUE NSA’s exploit leaked …
This week during the SSTIC2017 annual cyber security conference, a French conference running consecutively since 2004, the National Cybersecurity Agency of France (ANSSI) gave a presentation detailing their 2015 audit of their investigation …
Working Windows XP & 7 demos. #FRENCHMAFIA# Read More: Part 1 — Part 2 — Part 3 — Part 4 — @msuiche (Twitter)
In Short# DO NOT REBOOT your infected machines and TRY wanakiwi ASAP*!
*ASAP because prime numbers may be over written in memory …